


OSLO, Oct 18 — Chinese-made cars filmed sensitive information during a Norwegian military exercise, including access codes at secure sites and officials’ comings and goings, raising concerns about the risks posed by connected vehicles.
During a security exercise at Oslo airport on September 14-18, soldiers waiting in their vehicles and tapping on the onboard screens discovered videos recorded by the cars’ cameras, the Dagens Næringsliv (DN) newspaper reported.
The recordings showed who was getting in and out of the cars, the routes taken and even the codes used to open gates or doors to military facilities.
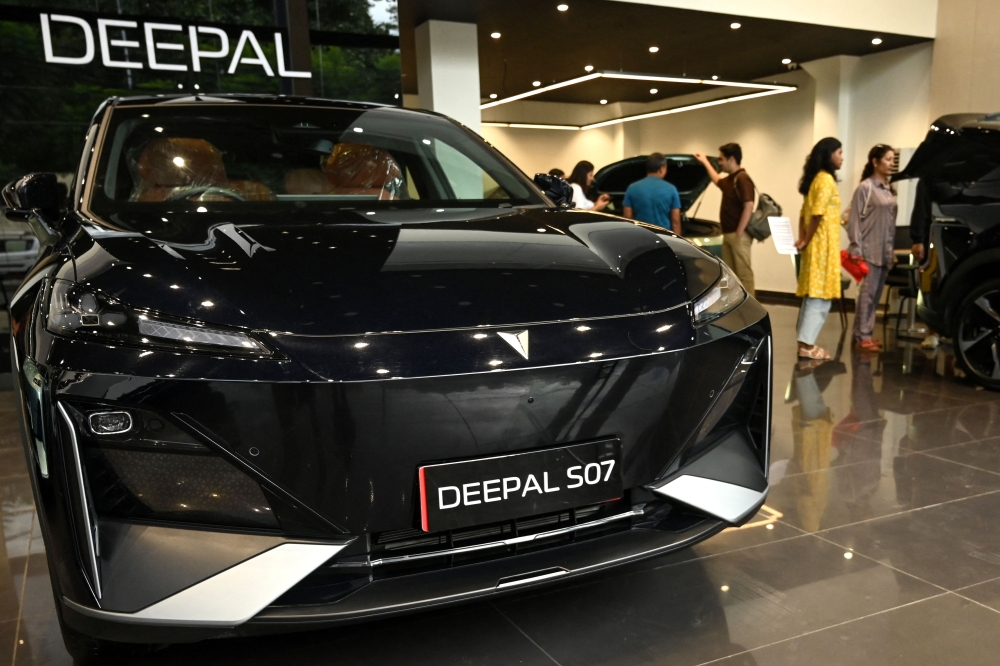
In its report three weeks after the exercise, DN said the recordings came from rental vehicles — at least two of them Deepal cars made by Chinese state-controlled automaker Changan.
The vehicles were supplied to the army by Hertz Norge, which is indirectly owned by Chinese automotive group Geely.
“Yes, soldiers from the Home Guard found videos from the vehicles’ sensors stored in their systems,” Lieutenant Colonel Per Gunnar Grosberghaugen, Norwegian Home Guard spokesman, confirmed to AFP.
It was not known whether the recordings had been shared with a third party, particularly in China, but the officer could not rule out the possibility.
The case highlights a paradox: while Europe’s armies are strengthening their defences against espionage and hybrid threats, the vehicles they use can collect sensitive information.
Even after discovering the leaks, the military continued using the vehicles until the end of the exercise because there were no alternatives, and the soldiers deleted the videos, DN reported.
Judging that a general ban on Chinese-made vehicles would be disproportionate to the potential security benefits, the military said it preferred security procedures tailored to each site, including possible local bans on vehicles equipped with cameras and sensors, regardless of their origin.
Hertz Norge stressed that it complies with Norwegian and European regulations.
“Our customers’ data is safe with us,” Hallvard Nerbovik, its marketing and communications director, told AFP.
“No personal data related to our rentals is shared with car manufacturers, our owners or other third parties without explicit legal grounds,” he added, without specifying whether the onboard videos might have been transferred.
Changan did not respond to AFP’s questions.
App spies
Last year, tests carried out for Oslo’s Ruter public transport authority revealed that Chinese manufacturer Yutong could theoretically remotely immobilise its electric buses through their “over-the-air” update system.
Norway could one day use the buses to evacuate the population during an emergency.
Ruter has since introduced mechanisms to monitor and delay incoming signals to control updates, it said.
Modern vehicles are not the only potential Trojan horses.
Smartwatches and fitness apps such as Strava, popular with joggers, can also expose sensitive military information.
In 2018, data published by Strava made it possible to identify military sites and soldiers’ routes, particularly in Afghanistan and Syria.
In March, French newspaper Le Monde was able to locate the French aircraft carrier Charles de Gaulle in almost real time in the eastern Mediterranean, thanks to a sailor on board who was using the app.
The Norwegian National Security Authority (NSM) said modern vehicles are “rolling computers that collect information”.
“We don’t know for sure where the information is sent or what it’s used for,” NSM official Andreas Skjold-Lorange told AFP.
The organisation, which is responsible for minimising strategic risks, including digital threats, said Norway should be wary not only of the data collected but also of excessive dependence on a single country.
This is particularly concerning if that country does not cooperate with Norway on security matters.
“If we become too dependent on services or products from a given country, that makes us vulnerable, whatever that country may be,” Skjold-Lorange warned. — AFP


